Malware & Ransomware
Stop Spyware: Practical Prevention Measures That Actually Work
Most spyware relies on voluntary permission rather than a break-in; revoking app access is the single most effective defence against data theft.
Most spyware relies on voluntary permission rather than a break-in; revoking app access is the single most effective defence against data theft.
Out-of-band patches bypass standard testing cycles to fix critical flaws, but they introduce unique stability risks that regular updates do not carry.
Routine maintenance prevents systemic failure by reducing the attack surface available to automated threats before human intervention is required.
Intrusion detection systems act as silent watchers, flagging suspicious network behaviour that firewalls often miss, turning invisible data flows into actionable alerts for your security team.
Identity management handles user access, while privilege management secures the temporary elevation of rights required for administrative tasks.
Most IoT compromises bypass network defences entirely by exploiting weak physical interfaces and unpatched firmware stored in non-volatile memory chips.
Blocking executables often bypasses control because scripts and interpreted files execute with the same privileges as native code, leaving lateral movement paths open.
Hardcoding secrets in code is the most common error, but even encrypted files fail if the decryption key is stored in the same repository.
Cached malicious responses linger in edge servers long after you fix the origin code, requiring explicit purges to stop the spread.
Your vendors hold keys to your digital doors, and standard contracts rarely cover what happens when their security fails or their data is scraped.
Most small businesses lose data not from hackers, but from accidental deletion and internal misconfiguration of cloud storage permissions.
Firmware flaws hide in hardware logic, making them invisible to standard operating system security scans and requiring specialised detection methods.
Attack surface reduction rules block specific execution paths rather than scanning file content, catching zero-day exploits that signature systems miss while risking legitimate application failures.
High alert volumes mask real intrusions by exhausting analyst capacity, turning your security stack into a source of operational noise rather than protection.
Profiling threat actors reveals the human and economic motives behind attacks, allowing defenders to prioritise risks based on behaviour rather than just technical signatures.
Most MFA failures occur not because the technology is broken, but because the implementation bypasses the authentication step for machine-to-machine traffic.
A password manager uses a single master key to encrypt all your credentials, making brute-force attacks computationally infeasible without it.
Information Sharing and Analysis Centres turn isolated incident data into collective defence, but membership demands operational discipline rather than passive observation.
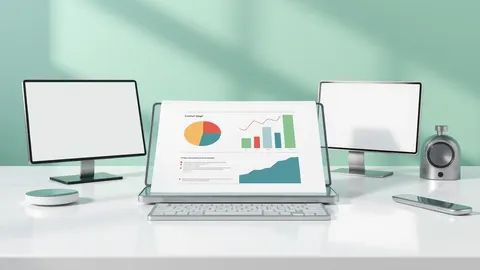
Threat intelligence reports transform raw data into actionable context, allowing you to distinguish between genuine threats and noise that would otherwise overwhelm your security operations.
Criminals now lease encrypted locks to amateurs, turning complex cyberattacks into standardised commercial products with shared risk.
The HIPAA Security Rule forces teams to document risk decisions, turning vague security hopes into auditable engineering choices that survive leadership changes.
Attackers hide behind legitimate cloud services, making standard firewall blocks ineffective and requiring deep packet inspection for true visibility.
Splitting your network limits damage from a single breach by creating invisible walls between devices, stopping attackers from reaching your most sensitive data.
Attackers bypass network rules by targeting the metadata endpoint directly from within the compromised instance, rendering external firewalls useless.